Building end to end
My experience is mostly on the infrastructure and security side. I now want to deliver visible projects, from scoping the need to going live — exactly how you work.
Application — Web development, AI & digital governance internship
M1 Cybersecurity student at Ynov Toulouse. I started in industrial automation, went through artificial intelligence, and now want to build web projects that can be understood, deployed and secured — from A to Z.
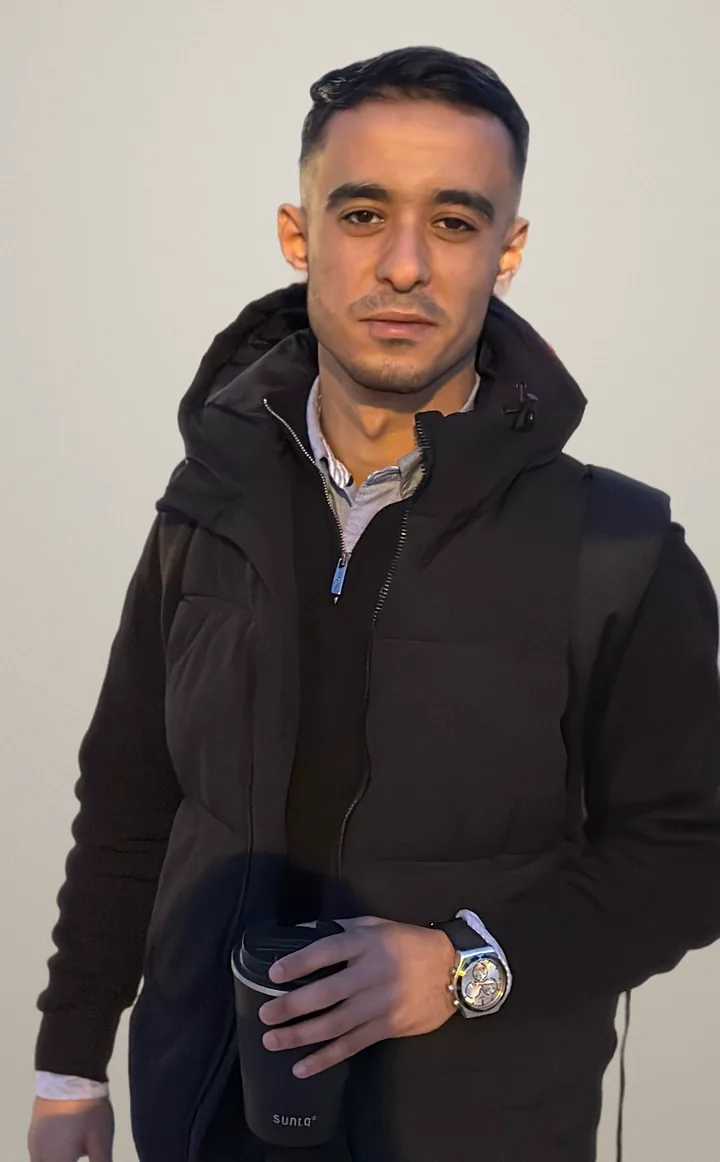
My path isn't linear, and that is what makes it coherent: industrial systems in Algeria, a degree in artificial intelligence from the University of Sussex, then cybersecurity at Ynov. At every step, the same question: how does this system really work, and what happens when you change it?
During my internship with KONITIX's security team, I took part in a production infrastructure migration. I learned a rule I now apply everywhere: listen first to the stated need, then suggest what the client hadn't considered yet — with at least two options, never just one.
This internship interests me because it brings together three things I want to practise together: building (the web), running (deployment and operations) and structuring (governance).
To break the ice: I run on coffee. If we meet, chances are I'll turn up with a cup in hand, just like in the photo. And if you know a good coffee spot in Toulouse, I'm all ears.
From industrial field work to information systems security.
PLCs, supervision and industrial systems. First lesson: a system running in production is never changed lightly.
Machine learning and AI fundamentals. What I mostly kept: knowing what a model does well, and recognising when it is confidently wrong.
Security architecture (TOGAF, NIST, Zero Trust, IAM, PKI), EBIOS RM risk analysis, GDPR, system hardening, AWS cloud security.
Migration of a Remote Desktop Services farm from Windows Server 2016 to 2022 (high availability, FSLogix profiles, SQL Always On). Acceptance testing, client meetings and technical documentation.
My experience is mostly on the infrastructure and security side. I now want to deliver visible projects, from scoping the need to going live — exactly how you work.
My AI degree taught me where these tools excel and where they make things up. Using them to go faster, yes; handing them the understanding, no.
Mapping, access rights, GDPR: that's the core of my studies. It's the part of the internship where I can be useful quickly, while I ramp up on Astro.
The web is the common thread; deployment and governance extend it. For each area: what you expect, what I bring, and what I still need to learn.
Personal and academic projects. Case studies are about fictional companies.
A small security monitoring centre on a Raspberry Pi 5 and my laptop: log collection, detection, dashboards. Next step: plugging in an ICS/SCADA honeypot, linked to my industrial background.
Website for a fictional ceramics manufacturer, rebuilt with AI from the structure of a real industry site: filterable catalogue, technical sheets, laid-tile preview, quote calculator. Visuals generated by code.
Visit the siteProfessional hardening report for Windows Server, Debian and Docker, written as a team, with a presentation deck.
Security architecture for a fictional healthcare SaaS migrating to AWS (Paris): TOGAF/NIST approach, functional, application and network diagrams, NIST SP 800-53 assessment.
Case study: Wazuh vs Microsoft Sentinel comparison, total cost of ownership, ROI, PKI and Azure Key Vault section, and an oral defence.
Ydays team project: GDPR compliance and risk analysis for a sports company. Directly linked to the governance part of the internship.
Astro, bilingual, no external dependencies, strict content security policy, deployed on Cloudflare Pages. And a few surprises for the curious.
The brief asks which AI tools were used, at which steps, and to distinguish my work from what was generated. Here is my approach, step by step.
Tool used: Claude (Anthropic), in conversation and in a development environment.
| Step | What the AI did | What I did |
|---|---|---|
| Reading the brief | Summarised both documents (offer and instructions) and spotted implicit expectations: method, autonomy, critical thinking. | Chose the angle: a cybersecurity profile that embraces the web as the common thread and governance as a strength. |
| Design | Proposed a structure, the stack (Astro) and design options based on two sites I showed it as examples. | Decisions: Astro (the company's stack), bilingual version, sober style, hidden mini-CTF. |
| Content | First draft based on the information I gave it about my background. | Proofreading, corrections and rewriting so that every sentence is accurate and in my voice. |
| Code | Generated the first version of the project: pages, components, styles, scripts. | Read the code, understood each file, made changes and fixes. |
| Going live | Explanations about Cloudflare Pages and security headers. | Created the GitHub and Cloudflare accounts, connected the repository, deployed and checked the live site. |
By default Astro inlines small scripts and stylesheets into the page, which a strict CSP blocks. I configured the build to externalise everything rather than weaken the policy with 'unsafe-inline'.
Texts live in two translation files; a single page renders them. Adding a language means adding a file.
No external fonts, no trackers, no CDN: the site is fast, and no visitor data goes to a third party.
Thank you for taking the time to browse this site. I would be glad to discuss it in person.